Why the Most Trusted Platforms Are Also the Easiest to Use
The most trusted digital platforms are consistently the most intuitive to use. The false choice between security and experience is a design problem, not a technical constraint, and it comes from security that arrives late.
The most trusted digital platforms are consistently the most intuitive to use. When security and compliance requirements are designed into the product architecture from day one, they become invisible to users while simultaneously building confidence. When they are added after the fact, they create friction that erodes both usability and trust at the same time. The false choice between security and experience is a design problem and not a technical constraint.
Most product teams believe that making something more secure means making it harder to use.
This assumption shapes thousands of product decisions every year. It produces authentication flows that feel like interrogation, consent screens that read like legal depositions, or error messages so vague that users cannot tell whether they did something wrong or the system failed them. And quite often the sense is that security is something being done to the user rather than for them.
The assumption is wrong. Or more precisely, it describes a symptom of poor sequencing rather than an inherent conflict between two legitimate goals.
The evidence points the other way. The Thales 2026 Digital Trust Index, which surveyed more than 15,000 consumers across 13 countries, found that login and sign-up problems are the primary driver of consumers abandoning digital services. The same research found that 45% of respondents preferred stronger security checks even if sign-ups took longer, compared with 22% who favoured faster access with lighter protections. What users cannot tolerate is security that is confusing, opaque, or arbitrary.
That distinction matters enormously for anyone building software in a regulated environment.
Why the False Choice Feels True
The myth of a security-experience trade-off is not invented from nothing. Product teams that have experienced it are not imagining things. They retrofitted a 2FA requirement onto an onboarding flow designed without it, and conversion dropped. They added cookie consent to a homepage designed without a consent layer, and the banner obscured the product. They also ran a KYC check at checkout for the first time, and users abandoned in significant numbers.
These are real outcomes from a real problem. But the problem is not security. It is late security.
When security, compliance, and trust requirements are layered on top of a product that was designed without them, they create friction because they interrupt flows that were never designed to accommodate them. The product’s UX logic was built on one set of assumptions, and the security requirements violate those assumptions at every touchpoint.
The alternative – designing for trust from the beginning – produces a completely different result. The authentication flow is part of the experience from day one rather than an interruption of it. The data consent screen explains genuinely useful things to the user rather than obscuring the product they came to use. The identity verification step feels like onboarding rather than an audit.
Trust as a UX Property
Trust is not a single moment. It accumulates across every interaction a user has with a product, and it depletes through the same mechanism (one interaction at a time).
The 2026 Liferay Broken Trust Report, surveying 1,000 users in December 2025, found that 75% will abandon a website that feels unsafe or behaves oddly, switching to a competitor to complete the same task. More tellingly, 61% say a single “off” moment changes how much they trust the brand, and 71% cite website reliability as a major factor in overall trust.
Notice what these findings describe: not security incidents, but moments when the product behaves unexpectedly or inconsistently. A page that loads differently on the second visit, a form that validates fields in a confusing order, or a confirmation email that arrives from a different domain than the product the user just signed up for. These are not security failures, they are design failures that destroy trust as effectively as a breach would.
Trust in a digital product is built through 3 overlapping signals that users evaluate (mostly unconsciously) across every interaction:
- Competence signals: does this platform do what it says it will? Does it work reliably, perform as expected, and handle errors predictably?
- Benevolence signals: does this platform respect my time, my intelligence, and my choices? Does it ask for only what it needs, explain what it is doing, and give me clear options?
- Integrity signals: does this platform do what it says? Does the privacy notice match actual behaviour? Does the consent flow reflect genuine options or dark patterns?
Security features contribute to all three categories when designed well. Biometric authentication delivers competence (it works every time) and benevolence (it is fast) simultaneously. A clear data deletion flow delivers integrity while a well-designed incident notification delivers honesty. The security feature and the trust signal are the same thing.
When Security Becomes Good UX
The clearest examples of security working as UX come from products that made a security process faster, more reliable, and more personal than the thing it replaced.
- Biometric authentication is the most widely experienced example. When smartphone manufacturers introduced fingerprint and face-based unlocking, they did not ask users to accept a security trade-off. They made unlocking faster, more reliable across all conditions, and more resistant to common attacks than the PIN it replaced. The security improvement was also the UX improvement. Both problems were solved by the same design decision.
- Single sign-on done well is another pattern that demonstrates this. When a product lets users authenticate through an identity provider they already trust – with clear, readable permission scopes and a one-click flow – the security outcome (delegating credential management to a specialist provider) is also the UX outcome (one less password, one less account, one less verification loop). The user does not experience security. They experience convenience built on a solid foundation.
- Payment checkout design shows the same principle at scale. The research is consistent: simplified, single-page checkout designs – where trust signals (secure connection indicators, recognizable payment brand logos, clear error handling) are integrated into the flow rather than interrupting it – consistently outperform multi-step flows that isolate the security steps. Baymard Institute estimates that optimizing checkout design can boost conversion rates by 35.26% for large e-commerce sites. The conversion gain comes directly from removing friction that was usually created by poorly integrated security steps.
- Government digital services offer a more complex example with high stakes. National digital identity platforms that have succeeded at scale did so by treating government services as products deserving the same design rigour as commercial software. The result was digital services that are more secure (because they use modern authentication standards rather than legacy shared passwords) and easier to use (because they were designed for the actual user, not for the administrator who needs an audit trail). In this case, the security requirements were the design brief, and the UX came from taking them seriously.
When Security Destroys Trust
The inverse pattern (security features that actively destroy trust) is less discussed but just as instructive.
- Cookie consent walls are the most widespread example. Designed to satisfy GDPR’s consent requirements, most implementations do the opposite: they obscure the product the user came to use, present choices that appear equal but are not, and bury the actual opt-out behind multiple steps. They satisfy a legal requirement while visibly violating the spirit of the regulation they were meant to implement. Users feel manipulated, not informed. The consent has been obtained, but trust has been damaged.
- CAPTCHA challenges follow the same pattern. A security mechanism designed to distinguish humans from automated bots has become a reliable signal that a platform does not trust its users. Worse, the most common CAPTCHA implementations are increasingly unreliable at their stated purpose – easily defeated by modern AI, but still challenging enough to frustrate real users with accessibility needs or slow connections. The security benefit is marginal; the UX cost is real.
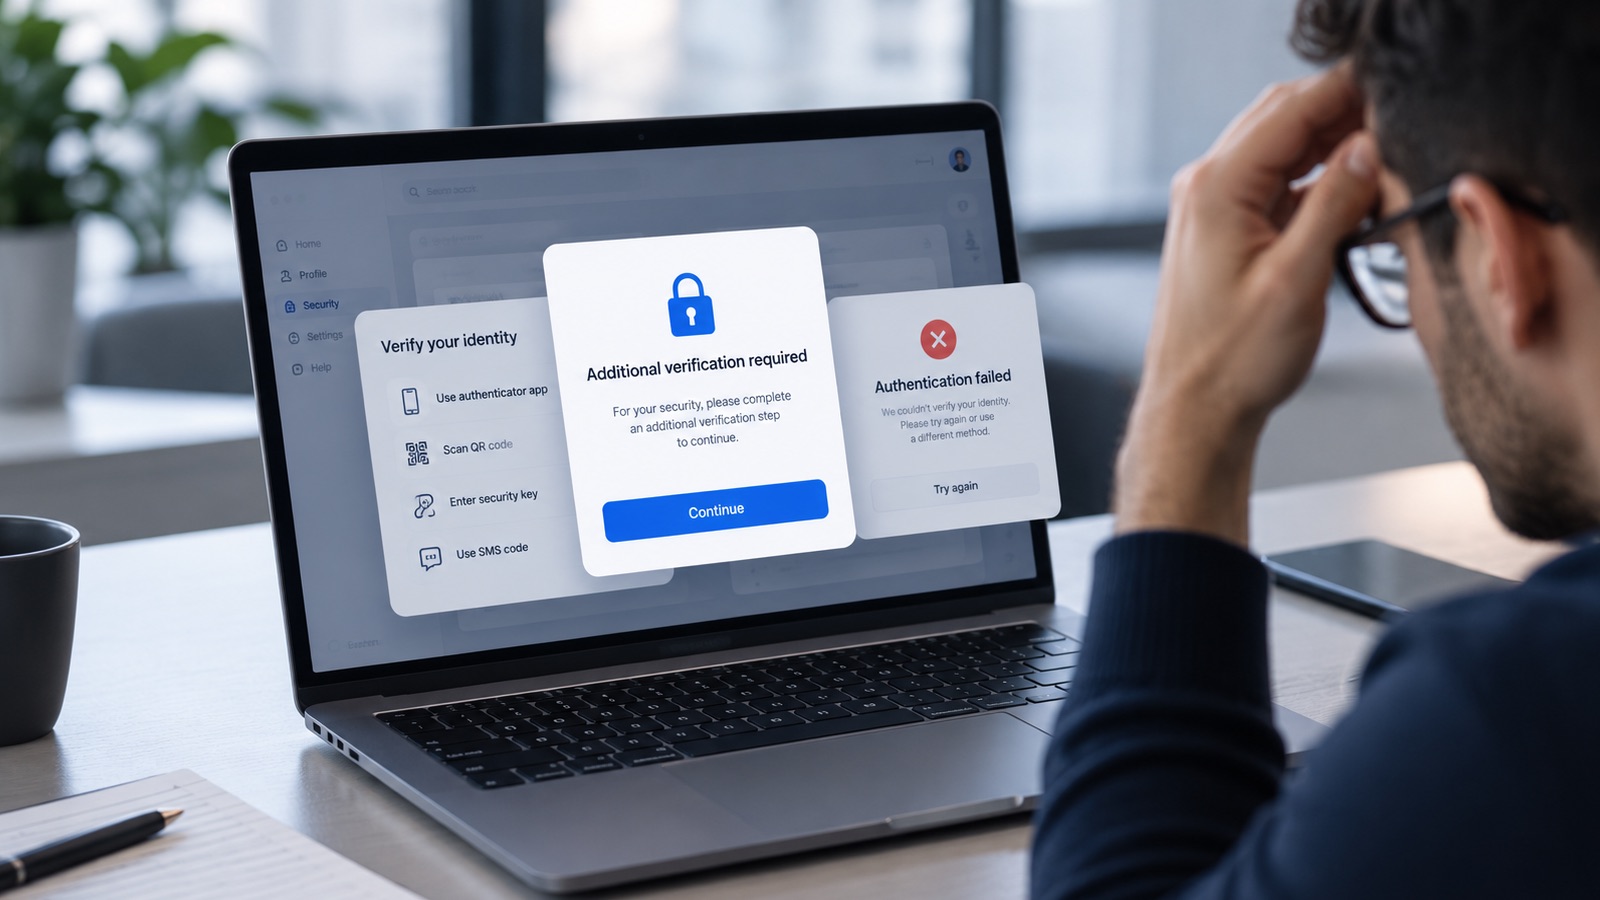
- Opaque authentication failures are a quieter trust killer. When a login attempt fails and the system returns only “incorrect email or password” – or worse, simply refreshes the page with no message at all – users are left unable to distinguish between a forgotten password, a mistyped email, an account that does not exist, or a system error. The opacity was introduced to prevent username enumeration attacks (a legitimate security concern), but the result is that users cannot troubleshoot their own access. The security intent is reasonable; the UX execution destroys confidence in the platform.
- Security questions as a fallback authentication mechanism represent perhaps the most complete example of security theatre that simultaneously damages trust. Questions about a mother’s maiden name or a first pet have near-zero entropy as security mechanisms – the answers are frequently guessable, findable through social media, or simply forgotten. But they signal to users that the platform is not taking security seriously while also being annoying to use. The worst of both outcomes.
Design Principles for Trust-First UX
The shift from “security as friction” to “security as experience” requires deliberate design decisions made early. These principles consistently appear in products that get it right.
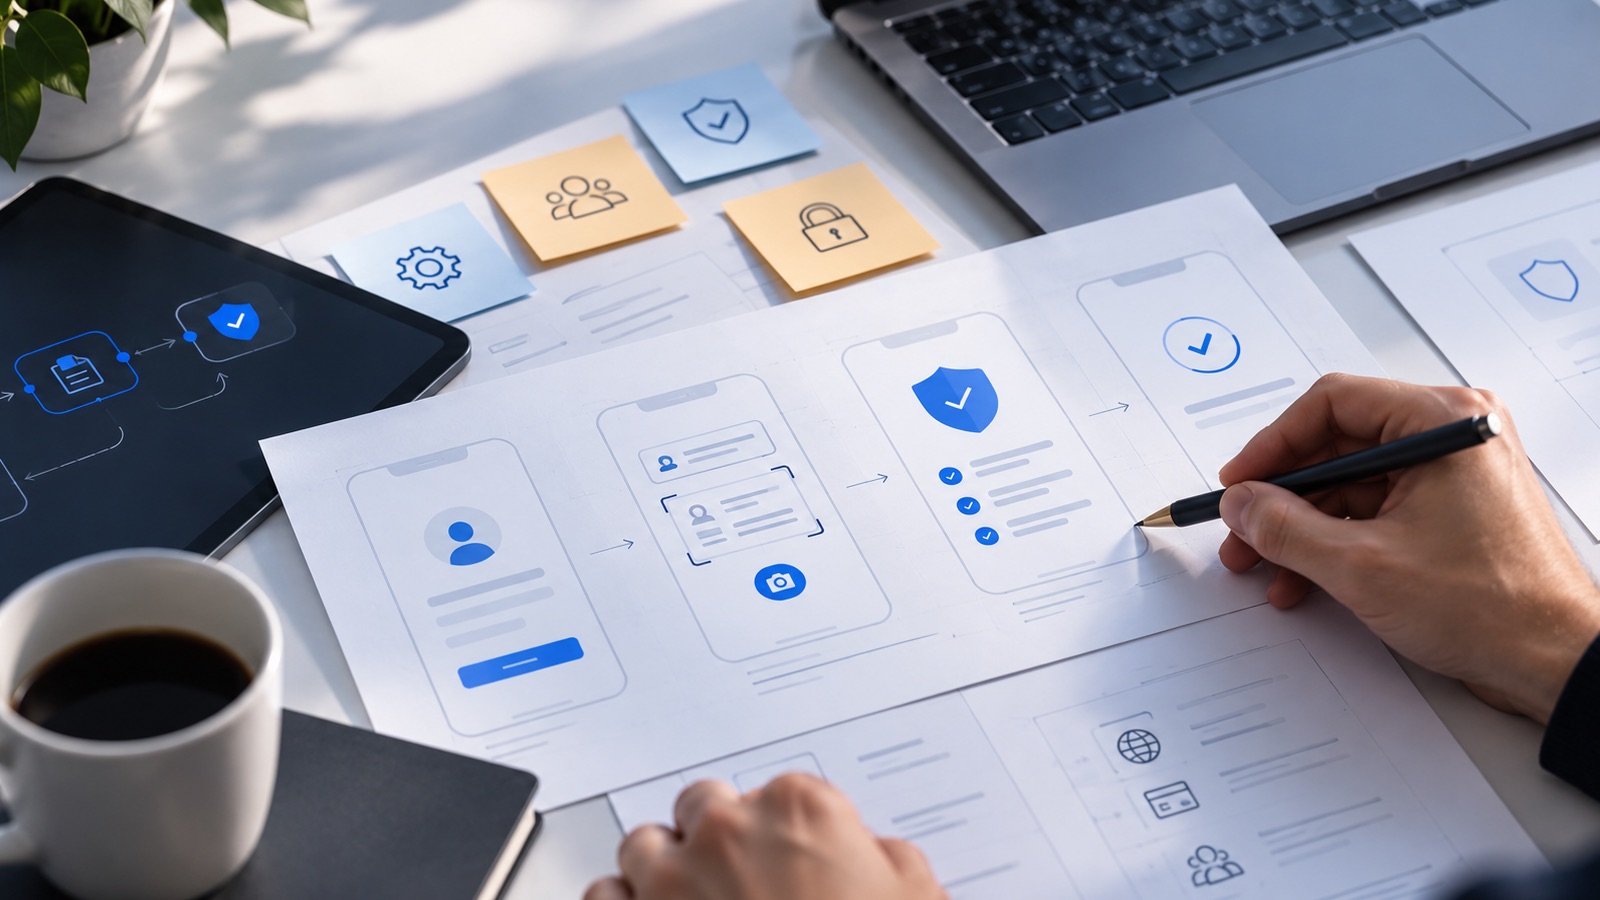
- Progressive trust: Ask for user trust incrementally, at the moment it is relevant and understood. Request location access when the user first tries a location-based feature, not at sign-up. Request document verification when the user attempts a transaction that requires it, not at account creation. Each request is contextualised, justified, and expected because it corresponds to something the user is actively trying to do.
- Minimum necessary footprint: The data you do not collect cannot be breached, subpoenaed, or misused. Products that request only what they need for specific, declared purposes are more trustworthy to users who notice this, and carry less liability for teams who understand the GDPR implications. The UX benefit is faster onboarding. The trust benefit is a smaller attack surface and a more defensible consent position.
- Clear consent language: Users do not read privacy policies. But they do notice when consent screens are written in plain language versus legalese. The platform that explains “we store your payment details with Stripe, a PCI DSS-certified provider, and never see your full card number” signals more trustworthiness than one that presents a 600-word addendum to its terms. Clarity is a trust signal.
- Transparent failure states: When something goes wrong – authentication fails, a transaction cannot be completed, a service is temporarily unavailable – the design decision to communicate clearly rather than generically is a trust decision. Users can tolerate failure. They cannot tolerate being left without information or recourse.
- Consistent security affordances: Trust is undermined when security behaviour is inconsistent. If the session timeout is different on mobile and desktop, users feel uncertain. If the 2FA code sometimes arrives immediately and sometimes takes 90 seconds, users lose confidence. Predictability is a form of trustworthiness, and inconsistency – even when the underlying security is sound – signals the opposite.
What This Means for Regulated Platforms
In fintech, healthtech, and regulated SaaS (where compliance requirements are mandatory) these design decisions stop being nice-to-have and become directly commercial.
Regulated platforms compete not just on features but on their ability to make compliance-adjacent flows (KYC onboarding, consent management, identity verification) feel normal rather than burdensome. The platform that makes document verification feel like part of onboarding – rather than a separate, anxious step – retains users that competing platforms lose.
The Thales 2026 Digital Trust Index found that sectors handling essential services and sensitive personal information retain stronger trust than consumer internet and media categories – suggesting that regulated environments create higher baseline expectations of trustworthiness that well-designed UX can actively deliver on, rather than fighting against.
The introduction of the EUDI Wallet changes this further. Platforms that integrate wallet-based identity verification into their onboarding flows as a first-class option – presenting it as the fast, government-verified path rather than an alternative to a familiar document upload – will demonstrate precisely this design philosophy in their most trust-critical moment. Users who try the wallet-based flow and find it faster, clearer, and more controlled than the document upload it replaced will not forget that experience.
The platform that builds that flow well earns trust that is very hard to buy back if lost.
| Design area | Questions to ask |
|---|---|
| Authentication design | Does your login flow explain itself? Can users diagnose their own authentication failures? |
| Consent and permissions | Are permission requests contextual (at point of use) or front-loaded at sign-up? |
| Security language | Is your consent copy written for users or for legal review? |
| Failure communication | When things go wrong, do users know what happened and what to do? |
| Trust signal consistency | Is your security behaviour consistent across devices, sessions, and user types? |
| Data minimisation | Could you explain to a user, in one sentence, exactly why you collect each data point you request? |
| KYC and identity flows | Does your verification flow feel like part of the product, or a gate in front of it? |
What To Do Next
The most trusted platforms did not build that trust despite their UX. They built it through their UX – through every authentication flow that worked, every consent screen that respected the user’s intelligence, every error message that told the truth.
If your product is treating security and experience as competing constraints, the problem is not the security requirement. It is the sequencing. The requirements that feel like friction are usually requirements that arrived late.
The right time to think about how trust is designed into your product is at the start – before the first sprint, before the component library is chosen, before the onboarding flow is sketched. That is what “Seek to Understand” means in practice: understanding the trust architecture before the product architecture, and designing them together rather than in sequence.
If you want to know where your product currently sits on that spectrum, that conversation starts with a discovery sprint.